Introducing AI Securely. Assessing Risks. Establishing Governance.
Artificial intelligence is changing how companies use data, make decisions, and automate processes. At the same time, requirements around security, governance, privacy, and compliance are increasing.
Consulteer InCyber helps companies introduce AI systems securely, transparently, and in a way that stands up to regulatory scrutiny. Our AI Security Consulting combines cybersecurity, AI risk management, AI governance, architecture expertise, and experience in operating modern security services.
The goal is not to slow down AI initiatives, but to enable them in a controlled way: with a clear strategy, sound AI risk assessment, appropriate security controls, and governance that works in day-to-day operations.
Employees often use AI tools productively before clear guidelines, approvals, or security controls are in place. The goal is to make this usage visible, assess the risks, and bring the use of AI into a controlled framework.
Attack Surface and new Threats
The integration of AI components, APIs, data sources, and external models expands the attack surface. Companies need clear security requirements to integrate AI systems securely into existing IT, cloud, and application landscapes.
Complexity and Regulation
The EU AI Act, data protection requirements, and internal compliance rules require clear guidelines for AI use, data handling, and the control of automated decisions. These requirements must be integrated into governance, risk management, and internal control systems at an early stage.
Transparency and Governance
The use of AI systems and autonomous agents requires new approval processes, responsibilities, and control mechanisms. This is the only way to make decisions traceable, manage risks, and clearly define responses to incidents.
Quality, Fairness and Ethics
AI systems can produce incorrect, biased, or opaque results. Companies need quality standards for AI outputs, procedures for assessing bias and fairness, and ethical guidelines for the responsible use of AI.
Our Top-down Approach
AI security does not begin with tools or individual security controls. It begins with a clear strategy, binding guardrails, and secure implementation in operations.
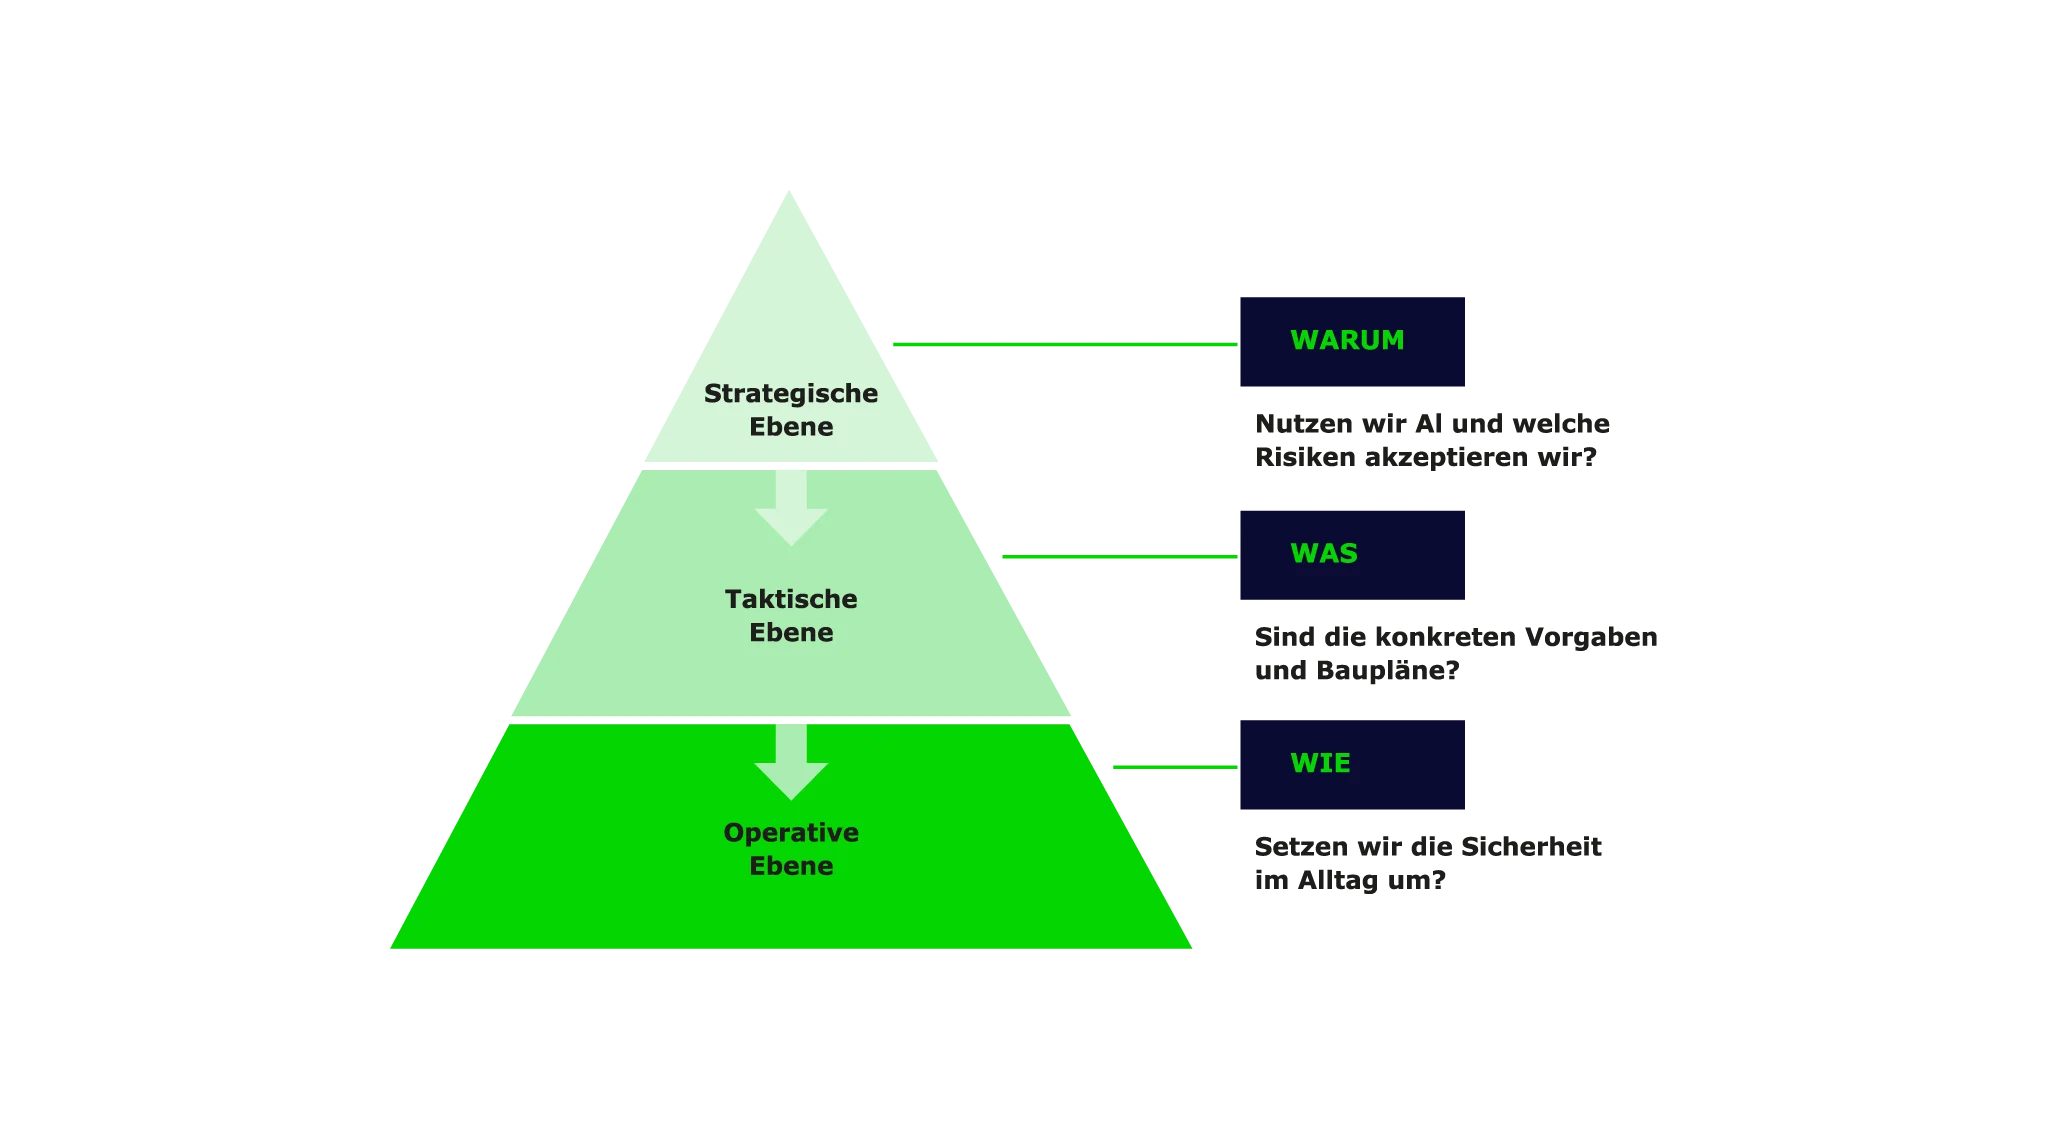
That is why Consulteer InCyber follows a top-down approach that considers AI security across three levels:
1. Strategic Level: Governance & Vision
Why do We use AI, and Which Risks are We Willing to Accept?
At this level, the foundations for the secure use of AI are established. Together with executive leadership and relevant stakeholders, we define objectives, responsibilities, and governance structures.
This includes:
Definition of AI governance
Assessment of regulatory requirements such as the EU AI Act, GDPR, or industry-specific regulations
Definition of the scope of AI use
Establishment of risk tolerances and security objectives
Embedding responsibilities and decision-making paths
The goal is to enable innovation without losing control, compliance, or transparency.
2. Tactical Level: Architecture & Standards
What are the Specific Requirements and Blueprints?
At this level, the strategy is translated into concrete requirements and security standards. The result is a set of guardrails for architecture, processes, and the secure use of AI systems.
This includes:
Definition of security requirements
Development of guardrails for AI systems
Classification of data and AI applications
Architecture requirements for models, APIs, and data flows
Integration of security-by-design principles
Definition of governance, approval, and control processes
This creates a consistent framework for the secure introduction and scaling of AI.
3. Operational Level: Risk & Implementation
How do We put Security into Practice?
At this level, the defined requirements are transferred into operational practice. The goal is to continuously monitor risks and embed security measures sustainably.
This includes:
AI risk assessments
Training and awareness measures
Monitoring of AI systems and models
Monitoring of anomalies and model drift
Documentation and evidence management
Support with audits and compliance requirements
This turns AI security into an integral part of daily operations rather than a one-off project.
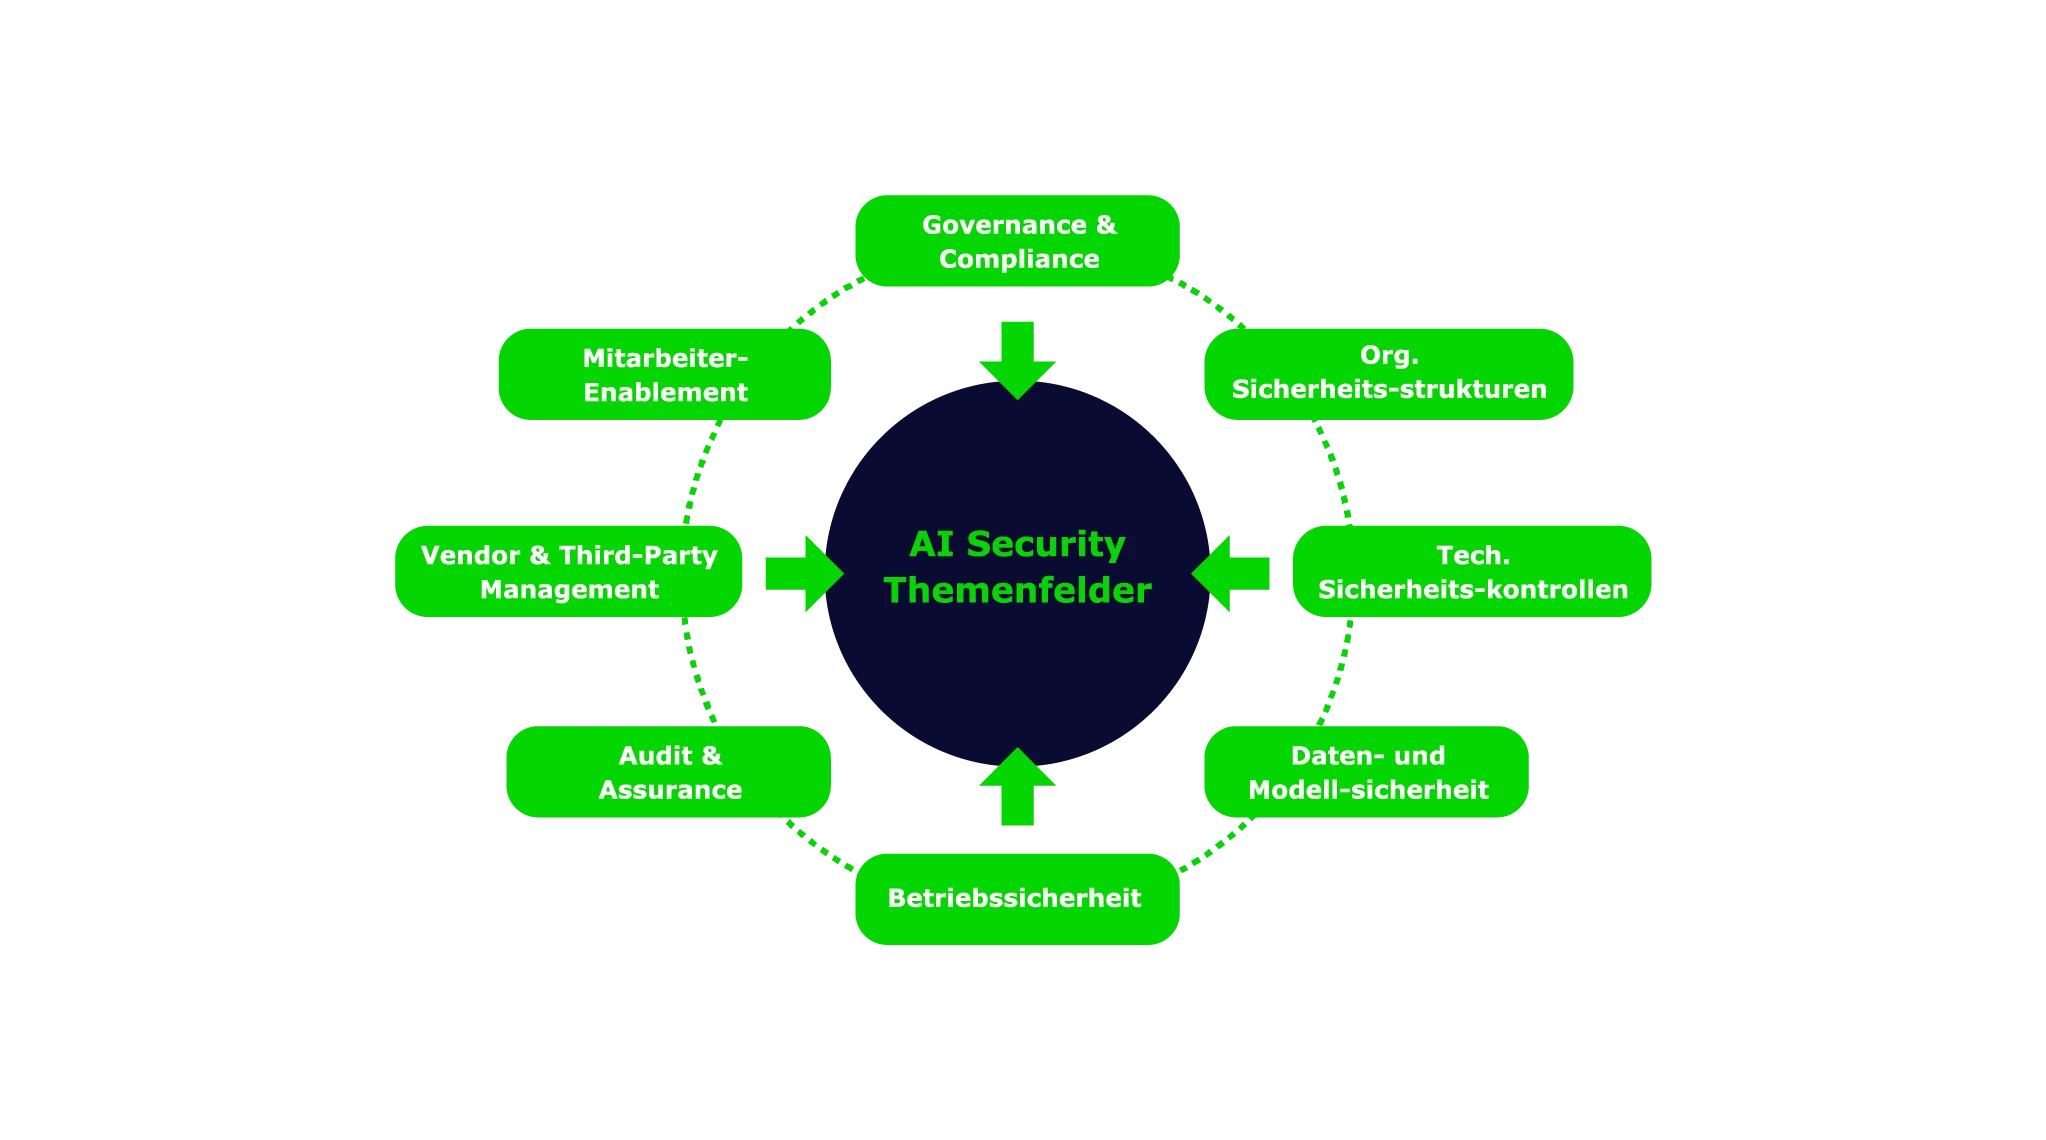
Our Focus Areas: A holistic Approach to AI Security
Our consulting approach covers the key dimensions of AI security – from governance and compliance to technical security controls and operational integration. These focus areas are aligned with recognised frameworks such as NIST AI RMF, ISO/IEC 42001, and industry best practices, helping organisations build secure, compliant, and scalable AI capabilities.
1. Governance & Compliance
Establishing clear governance structures for the secure and responsible use of AI. This includes AI boards or centers of excellence, roles and responsibilities, policies for AI use, and the classification of regulatory requirements such as the EU AI Act, GDPR, and ISO/IEC 42001.
2. Organizational Security Structures
Defining internal responsibilities for AI security, risk, and operations. This includes building AI security expertise, establishing clear decision-making paths and escalation processes, and defining roles for incident response, risk management, and compliance.
3. Technical Security Controls
Definition konkreter Security Requirements für KI-Systeme und KI-Anwendungen. Dazu gehören Least-Privilege-Prinzipien, Zugriffskontrollen, Guardrails für Prompts und Outputs, API Security sowie die sichere Integration in bestehende CI/CD-Pipelines und Betriebsmodelle.
4. Data & Model Security
Protecting training data, models, and AI applications against manipulation, data leakage, and uncontrolled use. This includes strategies against data poisoning, model inversion, unintended disclosure of sensitive information, and the protection of RAG architectures and intellectual property.
5. Operational Security
Establishing secure operating models for AI systems — from hosting strategies and monitoring to the continuous control of model behavior. This includes monitoring anomalies and model drift, defining clear incident response measures, and implementing processes for the secure operation of APIs, models, and agents.
6. Audit and Assurance
Establishing assessment processes to evaluate security, compliance, and effectiveness. This includes AI risk assessments, compliance checks, AI red teaming, security testing, model audits, and preparation for internal or external audits.
7. Vendor & Third-Party Management
Assessing AI vendors, external models, SaaS solutions, and third-party providers. This includes risk analyses, contractual security requirements, data protection requirements, and clear criteria for the use of external AI technologies.
8. Employee Enablement
Enabling employees to use AI securely in their daily work. This includes policies, training, and awareness around data input, prompting, transparency, approval processes, and the responsible use of AI tools.
Benefits
Clarity & Control
Gain visibility into existing AI systems, AI applications, data flows, and risks. At the same time, establish the governance structures, policies, and responsibilities required for the secure use of AI.
Security by Design
Through clearly defined security requirements, guardrails, and security controls, you ensure that AI systems, data, and architectures are designed and operated securely from the outset.
Auditability & Compliance
Establish governance frameworks and processes that support regulatory requirements such as the EU AI Act, GDPR, and ISO/IEC 42001. This makes AI initiatives transparent, auditable, and aligned with compliance requirements.
Risikominimierung & Enablement
Through clear policies, AI governance, and targeted employee enablement, you reduce risks such as shadow AI, data leakage, and misuse while promoting the secure adoption of AI technologies across the organisation.
Our Project Methodology
Phase 1: Foundations & Scoping
Phase 2: Assessment & Roadmap
Phase 3: Strategie, Governance & Architektur
Phase 4: Operationalisation & Enablement
We establish transparency around existing AI initiatives and define the scope for the assessment.
Key activities:
Regulatory scoping and identification of applicable requirements (EU AI Act, GDPR, NIST AI RMF)
Inventory of existing AI use cases and AI systems
Creation of an AI asset inventory
Identification of key stakeholders and responsibilities
Definition of scope, priorities, and target outcomes
Deliverables:
Scope definition and stakeholder overview
AI asset inventory
Assessment project plan
Our Tools & Accelerators: Enabling Faster and More Effective AI Security
To accelerate assessments and deliver practical outcomes, Consulteer InCyber leverages proven tools, checklists, and blueprints developed from real-world consulting engagements. These assets are aligned with recognised frameworks and standards such as NIST AI RMF, ISO/IEC 42001, and OWASP, helping organisations assess risks, prioritise actions, and make informed decisions around AI security and governance.
AI Governance & Security Readiness Check
The AI Governance & Security Readiness Check helps organisations assess the maturity of their AI governance and AI security capabilities. It is typically used during the assessment phase to establish a clear baseline and identify priority areas for improvement.
Focus: AI governance structures, privacy and data protection compliance, technical security controls, organisational responsibilities, and employee awareness.
Content: A structured assessment framework covering AI governance, AI risk management, security requirements, privacy, LLM security, and alignment with standards such as ISO/IEC 42001, NIST AI RMF, and OWASP guidance.
Outcome: A prioritised heatmap highlighting strengths, gaps, and areas requiring action, providing a clear foundation for an AI security roadmap.
AI Procurement & Deployment Blueprint
The AI Procurement & Deployment Blueprint supports IT, security, procurement, and architecture teams in evaluating new AI solutions, AI tools, and AI services before acquisition, deployment, or operational use.
Focus: Assessing the security, compliance, and suitability of AI technologies before implementation.
Content: A structured decision framework based on data classification, risk assessment, security requirements, vendor risk, deployment model, and intended data access.
Outcome: A clear decision-making basis for determining whether a proposed AI solution, external AI service, Large Language Model (LLM), or AI application is appropriate for the intended use case, security requirements, and data sensitivity level.
Talk to Our Experts
Do you want to adopt AI securely, assess AI risks, or establish reliable AI governance?
Consulteer InCyber is your reliable partner for AI Security Consulting – from the initial assessment through strategy and security architecture to operational implementation.
Get in touch with us, and together we’ll create a tailored cybersecurity solution for your business.
FAQs on Shadow AI
Which organisations is AI Security Consulting suitable for?
AI Security Consulting is suitable for organisations that want to use artificial intelligence securely, responsibly, and in line with regulatory requirements. It is particularly relevant for companies with early AI initiatives, Generative AI, AI agents, sensitive data, high compliance requirements, or existing shadow AI.
Regulated sectors such as financial services, healthcare, industry, public administration, and critical infrastructure also benefit from a structured approach. The goal is to introduce AI systems securely, identify AI risks early, and establish governance, compliance, and security measures across the entire AI lifecycle.
What is the difference between AI Security and AI Security Consulting?
AI Security refers to the measures, technologies, and security controls used to protect AI systems, AI models, data, and applications from misuse, manipulation, and uncontrolled access.
AI Security Consulting helps organisations plan these measures strategically, assess risks, and build governance structures for the secure use of artificial intelligence. While AI Security focuses more on technical protection, AI Security Consulting focuses on strategy, governance, risk management, compliance, and secure transformation.
Why is AI security relevant for organisations now?
AI security is becoming relevant because generative AI is changing not only business processes, but also the threat landscape. Phishing attacks have increased by 1,265 % due to generative AI, around 40 % of all email threats are already AI-supported, and the AI security market is growing at an annual rate of 24.2 %.
Organisations increasingly use AI systems in business-critical areas. This raises the need for governance, risk management, privacy, compliance, and security controls. AI security is therefore a central part of modern cybersecurity and digital transformation.
What security controls are important for AI systems?
The right security controls for AI systems depend on the use case, risk exposure, regulatory requirements, budget, and the organisation’s maturity level. Not every AI system requires the same security stack. A structured AI risk assessment is essential.
Key security controls include guardrails for prompts and outputs in Large Language Models, access controls for users, applications, and APIs, logging, monitoring, data governance, and policies for the secure use of AI technologies.
Defending against adversarial attacks requires filters against input manipulation. Protection against data poisoning requires validating and cleansing training data before model deployment, while controls against model inversion help prevent sensitive training data from being reconstructed from AI models.
Data governance also helps protect training data from poisoning, misuse, and theft. Model audits support the assessment of bias, fairness, transparency, and susceptibility to manipulation.
Why are risk and threat analyses important for AI systems?
AI systems have different attack surfaces than traditional IT systems. Risk and threat analyses are therefore a central part of AI Security Consulting.
Structured AI risk assessments help identify specific attack vectors for AI models, such as data poisoning, prompt injection, model inversion, adversarial attacks, or risks related to autonomous AI agents. At the same time, they assess potential impacts on data, business processes, compliance, and security.
AI red teaming can complement this by simulating real-world attacks on AI systems, Large Language Models, and AI applications to identify vulnerabilities early. As threats and AI technologies continue to evolve, regular AI risk assessments help organisations identify new risks early and continuously adapt security measures.
What expertise should an AI Security Consulting partner bring?
An AI Security Consulting partner should bring practical experience in artificial intelligence, machine learning, and modern cybersecurity. Key areas include AI governance, AI risk management, security architecture, AI models, Large Language Models, and relevant ML frameworks.
Before engaging a consulting partner, organisations should review concrete reference projects. Successfully completed projects securing Large Language Models, AI applications, or AI governance initiatives provide valuable evidence of a consulting firm’s actual expertise.
Especially in regulated sectors, the potential impact can be significant. A compromised AI system can influence business decisions, manipulate critical processes, or even falsify patient diagnoses in healthcare.
Why do machine learning models and AI technologies need dedicated governance controls?
Machine learning models and AI technologies differ from traditional software because their results depend heavily on training data, model behaviour, and context of use. This creates risks that traditional security controls alone cannot fully address.
A key issue is bias and fairness: biased training data can lead to discriminatory or incorrect results. Organisations therefore need to identify and reduce discrimination in training data and continuously review the quality of AI models.
Why are traditional cybersecurity and IT security often not enough for AI systems?
Traditional cybersecurity remains important. It covers network security, cloud infrastructure, identity and access management, application protection, and security operations. For AI systems, however, traditional IT security alone is often not enough because AI models, training data, prompts, outputs, and autonomous decisions create additional risks.
AI-specific threats include prompt injection, jailbreaks, data poisoning, model inversion, adversarial attacks, and manipulation of training data. Model poisoning can create backdoors for future attacks, while hostile inputs can deliberately cause AI systems to produce incorrect results.
In addition, AI systems change during operation. Continuous monitoring tracks model performance, anomalies, and model drift. Regular AI risk assessments help identify new threats early and continuously adapt security measures.
Organisations therefore need an extended AI security approach that combines traditional IT security with AI governance, data governance, risk and threat analysis, security controls, and clear incident response processes.
What role do governance, compliance, and experience play in AI Security Consulting?
AI Security Consulting combines technical security with AI governance, risk management, privacy, compliance, and experience in artificial intelligence. Regulatory requirements demand governance across the entire AI lifecycle and comprehensive risk management.
The EU AI Act requires organisations to assess and manage risks related to AI systems. ISO/IEC 42001 defines requirements for AI security management systems and supports the development of structured governance frameworks. The goal of good consulting is not long-term dependency, but enabling the internal team.
What should organisations consider before using AI systems?
Before using AI systems, organisations should clarify key considerations around data, access, models, compliance, and incident response.
Relevant questions include: What information is being processed? What AI risks exist? Who is responsible? Which regulatory requirements apply? How are results monitored? And what response is planned if an AI system behaves unexpectedly?